First, What is DNS?
Think of the Domain Name System (DNS) as the internet's phonebook. When you type a website address like 'google.com' into your browser, your computer doesn't know where to go. It sends a request to a DNS server, which looks up 'google.com' and translates it into a numerical IP address (like 172.217.168.238) that your computer can use to connect. By default, your device uses the DNS servers provided by your Internet Service Provider (ISP).
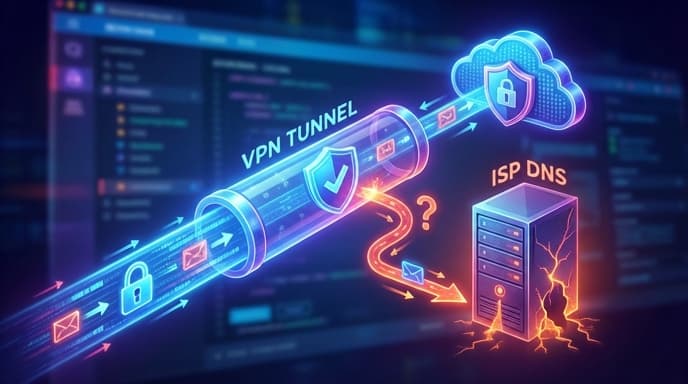
How a DNS Leak Happens
When you connect to a VPN, it's supposed to create a secure, encrypted tunnel for *all* your internet traffic. This includes your DNS requests. Instead of asking your ISP's DNS server for directions, your computer should ask the private, anonymous DNS server run by your VPN provider. A DNS leak occurs when, for various reasons, your computer ignores the VPN tunnel and sends its DNS request directly to your ISP's server. Your main web traffic (the data from the website itself) might still be encrypted by the VPN, but the initial 'phonebook lookup' happens out in the open.
This can happen due to poor configuration of your operating system, browser settings, or if your VPN software is not properly equipped to prevent it.
Why Is a DNS Leak a Privacy Risk?
A DNS leak creates a detailed log of your browsing history that is visible to your ISP. Even though the content of your traffic is encrypted, your ISP can see every single website you visit. For example, they might not see what you posted on a specific forum, but they will know you visited that forum. This record of your browsing activity can be logged, sold to advertisers, or handed over to government agencies. It completely undermines the privacy you're trying to achieve by using a VPN in the first place.
How to Test for and Fix a DNS Leak
The good news is that testing for a leak is easy, and most modern, reputable VPNs have built-in protection.
- Test for a Leak: Disconnect from your VPN and Google 'what is my IP'. Note the IP address and your ISP's name. Now, connect to your VPN. Then, visit a site like `dnsleaktest.com` or `browserleaks.com/dns`. Run the test. If the results show servers belonging to your actual ISP instead of your VPN provider, you have a leak.
- Enable Leak Protection: Dive into your VPN application's settings. Look for an option called 'DNS Leak Protection' or 'Prevent DNS Leaks' and make sure it is enabled. Most premium VPN services have this feature turned on by default.
- Use a Reputable VPN: The single best way to prevent DNS leaks is to use a high-quality, paid VPN service that operates its own DNS servers and has robust leak protection built into its software. Free VPNs are often the worst offenders when it comes to leaks and privacy issues.
Frequently Asked Questions
Is a DNS leak the same as an IP leak?
They are related but different. An IP leak exposes your true IP address, revealing your location. A DNS leak exposes your browsing activity (the sites you visit) to your ISP. Both are serious privacy flaws.
Does a VPN kill switch prevent DNS leaks?
A kill switch is designed to block all internet traffic if the VPN connection drops, which prevents IP leaks. While it's a crucial feature, dedicated DNS leak protection within the VPN app is what specifically addresses the DNS query issue.
Can my browser cause a DNS leak?
Yes, some browsers have features like DNS pre-fetching that can sometimes bypass the system's network settings and cause leaks. Using a VPN with strong, system-wide leak protection is the best defense.
Key Takeaways
- DNS is the 'phonebook of the internet,' translating domain names into IP addresses.
- A DNS leak occurs when your DNS requests bypass your VPN's encrypted tunnel, going directly to your ISP.
- This allows your ISP to see and log every website you visit, even with a VPN active.
- You can check for leaks using online testing tools like `dnsleaktest.com`.
- The best way to fix and prevent leaks is to use a reputable VPN with built-in DNS leak protection enabled.